Skip to content

New guideModernizing a legacy system without stopping the business

11 — Application Security

Security designed into the software, not added at the end.

Most breaches in business software come from ordinary gaps: weak access control, exposed configuration, outdated dependencies, unvalidated input. We design systems to avoid them from the first architecture decision, and review and harden existing applications that handle customer, financial or personal data.

Capabilities

What this service covers.

  1. 01

    Secure architecture

    Threats considered during design: data flows, trust boundaries and failure modes.

  2. 02

    Identity and access

    Authentication, session management and role-based access control.

  3. 03

    Code review

    Review for common vulnerability classes (OWASP Top 10).

  4. 04

    Dependency management

    Automated scanning and updates for third-party packages.

  5. 05

    Configuration hardening

    Headers, secrets, network exposure and cloud permissions.

  6. 06

    Data protection

    Encryption in transit and at rest, and data minimisation.

What We Build

Cybersecurity solutions we deliver.

Secure architecture, access control and hardening for business systems.

Example Cybersecurity interface built by Eryon
  • 01

    Secure architecture review

    Threats, trust boundaries and data flows assessed before build.

  • 02

    Application security review

    Code and configuration reviewed against the OWASP Top 10.

  • 03

    Authentication and SSO

    Secure login, MFA and single sign-on integration.

  • 04

    Role-based access control

    Permission models designed with scopes and audit trails.

  • 05

    Dependency and vulnerability management

    Automated scanning and update routines.

  • 06

    Cloud security hardening

    IAM, network exposure, secrets and logging reviewed and fixed.

  • 07

    Data protection

    Encryption, retention and data minimisation built into the system.

  • 08

    Remediation

    Fixing the issues found, not just reporting them.

Use Cases

When clients bring us in.

Before a major launch

A review of a new system before real users and data arrive.

Handling sensitive data

Health, financial or personal data that needs stronger controls.

Inherited codebase

An application built by others that nobody has reviewed.

Customer security questionnaires

Enterprise buyers asking how your system is protected.

Where It's Used

Problems we solve, sector by sector.

  • Healthcare

    The problem
    Staff and patient data needs strict access control.
    What we build
    Role-based access with audit logging and encrypted storage.
  • Financial services

    The problem
    Customers and auditors ask for evidence of controls.
    What we build
    Documented controls, access reviews and secure delivery pipelines.
  • SaaS companies

    The problem
    Enterprise buyers send long security questionnaires.
    What we build
    Hardened architecture and clear answers backed by real controls.
  • E-commerce

    The problem
    Admin panels and payment flows are attractive targets.
    What we build
    Hardened admin access, rate limiting and tokenised payments.
  • Education

    The problem
    Systems hold minors' personal data.
    What we build
    Data minimisation, consent handling and restricted access.
  • Inherited codebases

    The problem
    Nobody knows how secure the existing system is.
    What we build
    A prioritised security review followed by remediation.

Recognise your situation here?

Talk to an engineer

How We Deliver

Delivery you can plan around.

Scoped review

Agreed scope, method and reporting format before starting.

Prioritised findings

Issues ranked by risk with clear remediation steps.

Fixes, not just reports

We can implement the remediation as well.

Re-verification

Fixed issues checked again before closing.

Deliverables

  • Security review report
  • Remediation plan
  • Access control model
  • Hardened configuration
  • Security guidelines for your team

Technology Stack

Tools we use for this work.

  • Spring Security
  • JWT / OAuth 2.0
  • OWASP guidelines
  • Dependency scanning
  • TLS
  • Cloud IAM
  • Docker

Security & Scalability

  • Least privilege

    Users, services and integrations get only the access they need.

  • Defence in depth

    Controls at the interface, API, database and network.

  • Auditability

    Security-relevant actions logged and retained.

  • Secure delivery pipeline

    Checks run automatically on every change.

Process

From first workshop to production.

  1. 01 · Discover

    Workshops with the people who run the process today. We map how work actually moves, where it stalls and what the system must never get wrong.

  2. 02 · Define

    A written scope: users and roles, core workflows, integrations, non-functional requirements and a release plan you can hold us to.

  3. 03 · Architect

    Data model, service boundaries, hosting, security model and the trade-offs behind each choice — reviewed with your team before code starts.

  4. 04 · Build

    Short sprints with a working demo every week. Code review on every change, automated tests on the paths that carry money or data.

  5. 05 · Validate

    Functional QA, role-by-role acceptance, performance checks and a security pass before anything reaches production users.

  6. 06 · Scale

    Staged rollout, monitoring and a support window. Then the backlog of improvements that only real usage reveals.

Related Case Studies

Where we've done this before.

Healthcare · Web

Hospital HRMS

Workforce management for hospital staff

Challenge
Hospital HR ran across fragmented systems, causing shift conflicts and slow communication with clinical staff.
Solution
A centralized HRMS with role-based access, rota planning, attendance, leave and document management built for clinical shift patterns.
Outcome
Shifts, leave, attendance and staff records in one secure system instead of several disconnected tools.
Technology
  • Next.js
  • Spring Boot
  • PostgreSQL
  • MongoDB
  • Redis
  • Docker
Read the case study

Professional Services · Web

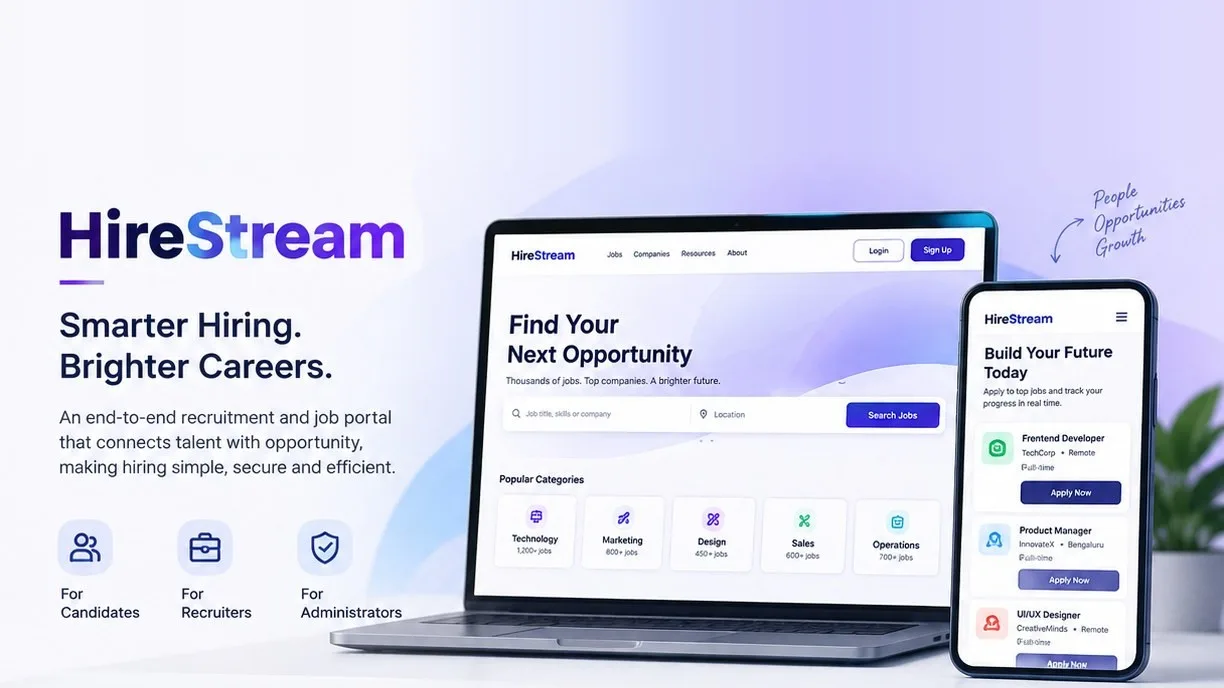
HireStream

Recruitment portal for employers and candidates

Challenge
Hiring ran on scattered email threads and spreadsheets, so applications were lost and pipelines mismanaged.
Solution
A recruitment portal with a Spring Boot REST API, JWT-secured roles for recruiters and candidates, and status tracking.
Outcome
Job posting, applications and candidate tracking moved out of email threads into one secure portal.
Technology
  • Java
  • Spring Boot
  • MySQL
  • Spring Security
  • JWT
  • React
Read the case study

FAQs

Common questions.

Do you provide compliance certification?

No. We are not a certification body. We design and build software to support your compliance programme and can work alongside your auditors.

Can you review software someone else built?

Yes. We review code, configuration and infrastructure, then report findings with prioritised fixes.

What standards do you follow?

We use the OWASP Top 10 and OWASP ASVS as reference points for application security reviews.

Can you fix the issues you find?

Yes. Remediation can be part of the engagement.

What does an application security review include?

Review of authentication, access control, input handling, configuration, dependencies and data protection, with findings ranked by risk and clear fixes.

Do you help with SOC 2 and GDPR readiness?

Yes. We implement the technical controls these frameworks expect — access control, logging, encryption, change management — and work alongside your auditors or advisers.

How often should we review application security?

At least before major releases and after significant architectural changes, with automated dependency scanning running continuously.

Do you provide penetration testing?

Our focus is secure design, review and remediation of the applications we build or maintain. For formal penetration tests we can prepare the system and fix the findings.

Planning a project
like this?

Tell us what the system needs to do. We'll reply within 24 hours with questions, not a sales script.